Board training
12 min read
DORA Board Training Requirements: Article 5(4) Explained
What directors need to learn, how often to revisit it, and how to turn training records into evidence of informed decisions.
Read the guide ↗THE BOARDROOM BRIEF
Practical guides for the leadership of financial entities within DORA’s scope. Strengthen oversight of digital operational resilience across cyberattacks, system failures and third-party disruptions.
Read the guide ↗
DORA · Executive guide
Board trainingWhat directors need to learn, how often to revisit it, and how to turn training records into evidence of informed decisions.
Read the guide ↗A practical guide to governing ICT risk: what to approve, what to challenge, and how to follow decisions through to completion.
A supplier register is a starting point. Effective oversight connects the contract to the business service, the recovery evidence and the decision the board needs to make.
A fictional disruption, three decision rounds and evidence you can use to improve the next response. Designed for directors and senior executives of financial entities.
A practical guide to turning operational resilience data into decisions that directors can understand, challenge and follow through.
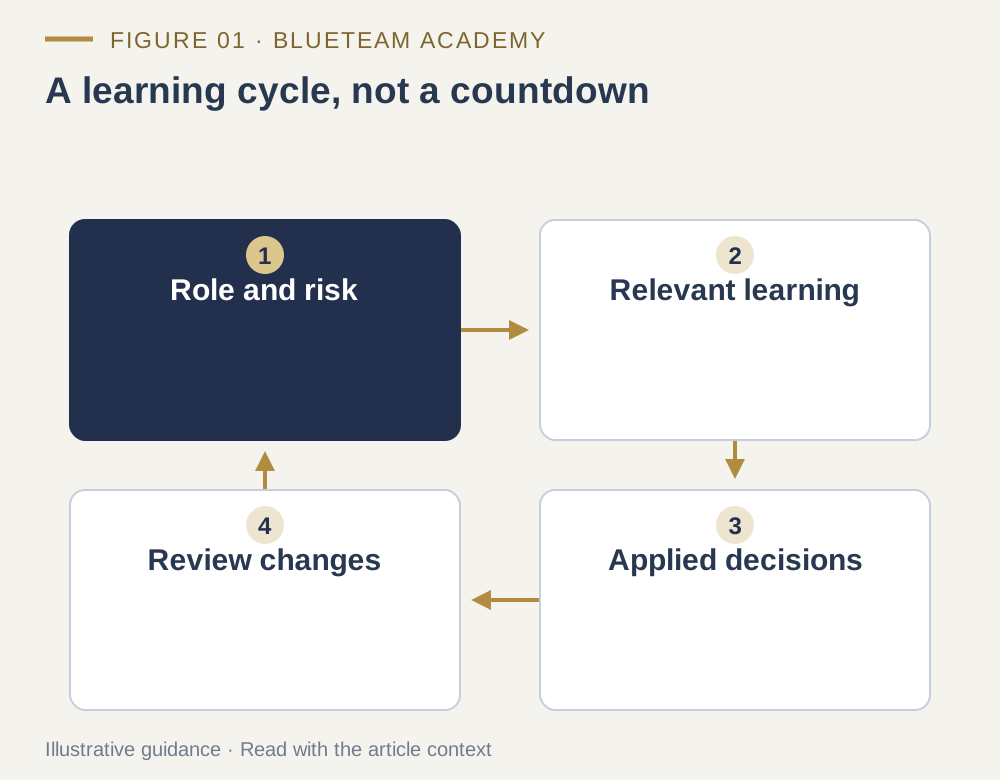
Build a regular learning cycle that responds to risk, role and change. An annual course can be a starting point; it is not the whole decision.
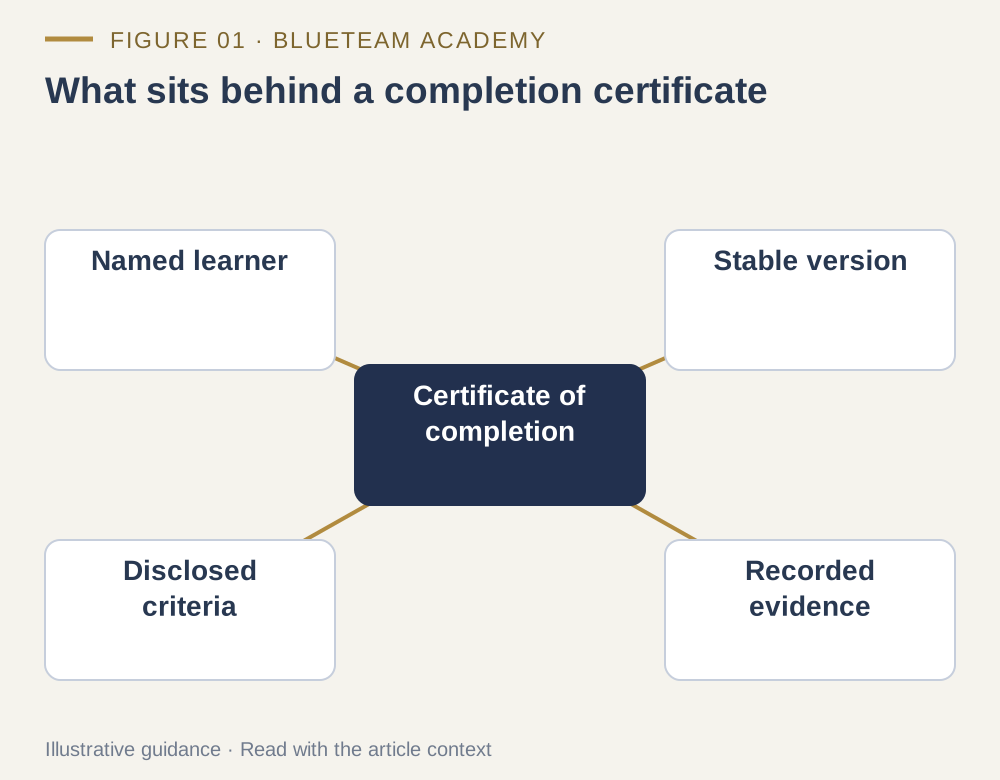
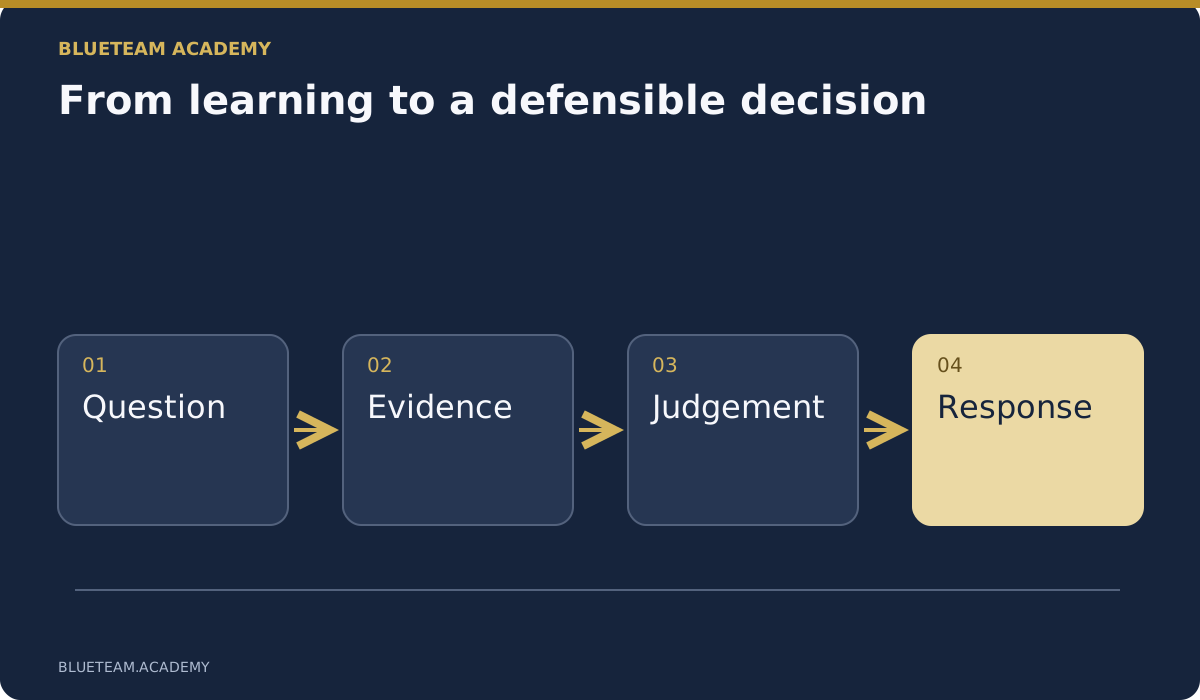
A useful certificate identifies the learning that happened. A defensible evidence record also shows the criteria, version, decisions and gaps behind it.
Choose credentials for the work your defenders actually do. Compare certification routes, build practical skills, and keep clear evidence of who completed what.
A practical guide for SOC leaders, responders and IT managers: choose training that turns alerts into defensible decisions, then prove the team can apply it.